
Updated Nov 2026
Administrator accounts have elevated access to Google Workspace settings, users, and organizational data. If these privileges are broader than necessary, a compromised admin account can create significant security risks.
Regular Google Workspace admin role audits help IT teams identify excessive permissions, review privileged accounts, and maintain appropriate access controls.
This is Part 2 of our 10-Step Google Workspace Auditing Guide. In Part 1, we covered access management. Here, we’ll focus specifically on administrator privileges.
Quick Answer: How Do You Audit Admin Roles in Google Workspace?
To audit Google Workspace administrator roles, open the Google Admin console > Account > Admin roles. Review Super Admins, delegated administrators, custom roles, and their assigned privileges. Confirm that each administrator requires their current access, remove unnecessary permissions, and review Admin log events for changes to administrator roles. Repeat these checks regularly and document your findings.
How to Audit Administrator Roles in Google Workspace
Follow these five steps to review administrative access.
1. Identify All Administrators
In the Google Admin console, navigate to Account > Admin roles.
Review the available roles and their assigned administrators, paying particular attention to:
- – Super Admins: Accounts with extensive administrative control across Google Workspace.
- – Prebuilt administrator roles: Roles such as User Management Admin and Groups Admin.
- – Custom administrator roles: Roles created with selected privileges for specific responsibilities.
You can also open an individual account under Directory > Users > Admin roles and privileges to review its assignments.
2. Review Assigned Privileges
Determine whether each administrator needs the permissions they currently hold.
Ask:
- – Does this administrator still perform the tasks associated with the role?
- – Could a more limited role provide sufficient access?
- – Are custom roles granting unnecessary permissions?
- – Are any former team members or inactive accounts still assigned administrator privileges?
Apply the principle of least privilege by granting only the permissions necessary for each responsibility.
3. Review Organizational Unit Restrictions
Not every administrator needs permissions across the entire organization.
Google Workspace supports organizational unit (OU) scoping for certain delegated administrator privileges. This allows administrators to manage supported resources within assigned OUs rather than across the entire domain.
Google has also expanded granular ChromeOS device administration capabilities, including OU-scoped device management privileges.
When reviewing roles, check whether you can limit administrative responsibilities to specific OUs and whether existing assignments are broader than necessary.
Important: OU scoping isn’t available for every administrative privilege. Review the scope supported by each role before making changes.
4. Investigate Administrator Activity
Role assignments show what administrators can do. Audit logs help you investigate what they have done.
Navigate to Reporting > Audit and investigation > Admin log events in the Google Admin console.
Review relevant events, including:
- – Administrator role assignments and removals.
- – Changes to security settings.
- – User account management actions.
- – Other significant administrative configuration changes.
Investigate unexpected changes and verify that sensitive actions were authorized.
Available event details and investigation capabilities depend on your Google Workspace edition and administrator privileges.
5. Remove Unnecessary Access and Document Changes
After reviewing privileges:
- Remove outdated administrator assignments.
- Replace overly broad roles with more appropriate delegated or custom roles.
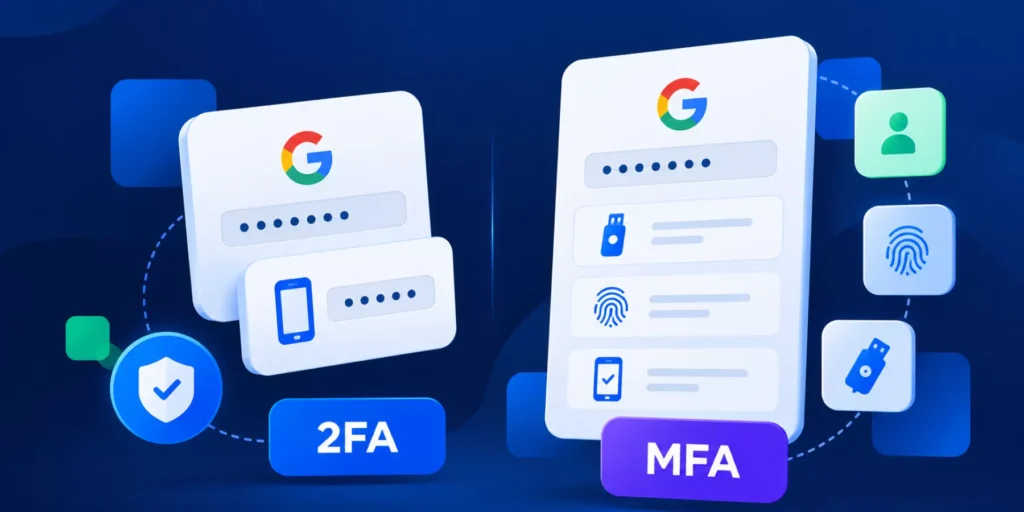
- Verify that privileged accounts use strong authentication.
- Document changes, approvals, and any exceptions.
Review the results after changes are applied to confirm that administrators retain the access required for their responsibilities.
Google Workspace Administrator Role Audit Checklist
Use this checklist during your next review.
| Audit Area | What to Check |
|---|---|
| Super Admins | Number of accounts and business justification |
| Delegated roles | Permissions aligned with current responsibilities |
| Custom roles | Excessive or outdated privileges |
| OU restrictions | Whether supported roles can be scoped more narrowly |
| Inactive accounts | Former employees and unused administrator access |
| Authentication | 2-Step Verification and phishing-resistant MFA |
| Admin activity | Unexpected role assignments and configuration changes |
| Follow-up | Access removal, documentation, and recurring reviews |
Download our Google Workspace Auditing Task List for a reusable reference.
Best Practices for Managing Administrator Privileges
Beyond scheduled audits, administrators should follow a few ongoing practices.
- – Limit Super Admin access. Reserve these privileges for accounts that genuinely require full administrative control.
– Use delegated and custom roles. Assign specific permissions instead of granting broad access for routine tasks.
– Protect privileged accounts. Require strong authentication, preferably phishing-resistant methods such as security keys or passkeys where supported.
– Review changes regularly. Audit privileged access quarterly and whenever employees change roles or leave the organization.
– Investigate unusual activity. Use available audit logs and security alerts to identify unexpected administrative actions.
These practices support a Zero Trust approach to Google Workspace security, where access is limited and regularly reviewed.
How GAT Labs Supports Least-Privilege Administration
Google Workspace provides native administrator roles and auditing capabilities. GAT Labs adds options for delegating specific auditing tasks without granting broader Google Workspace administrative permissions.
With GAT+ Delegated Auditors, organizations can assign selected GAT+ auditing capabilities to authorized users without making them Google Workspace Super Admins.
This allows teams to distribute supported auditing responsibilities while maintaining more limited access to the Google Admin console.
GAT+ also provides auditing and reporting capabilities to help administrators investigate user activity and access risks across Google Workspace.
Keep Administrator Access Under Review
Administrator role audits help organizations identify excessive privileges, investigate sensitive changes, and maintain control over who can manage Google Workspace.
Start by reviewing Super Admin accounts, then examine delegated roles, custom permissions, and administrator activity. Document the findings and establish a recurring review schedule.
Insights That Matter. In Your Inbox.
Join our newsletter for practical tips on managing, securing, and getting the most out of Google Workspace, designed with Admins and IT teams in mind.